A customer or auditor is asking
You may need SOC 2, ISO 27001, a customer questionnaire or evidence that your controls are operating effectively.
Security, privacy and assurance
J-SAS helps organizations understand which requirements apply, map overlapping obligations and turn them into security and compliance work that can actually be maintained.
Start with the business need
The best starting point is not always the framework with the most familiar name. It is the customer request, legal obligation, business objective or security risk that your organization needs to address.
You may need SOC 2, ISO 27001, a customer questionnaire or evidence that your controls are operating effectively.
Privacy, health, financial-services or critical-infrastructure obligations may shape what your program must cover.
NIST, CIS or a practical control baseline can help organize priorities before a certification or audit is required.
Supported requirements
These requirements are not interchangeable. Some are standards, some are laws, some are assurance programs and others are buyer or sector expectations. We help clarify the difference and build the right response.
ProtechSuite includes support for widely used frameworks and can be configured for custom controls, customer requirements and internal standards. The right scope is confirmed during assessment.
Prepare the controls and evidence needed for an independent SOC 2 examination based on the applicable Trust Services Criteria.
Explore SOC 2 servicesEstablish, operate and improve an information security management system in preparation for certification.
Organize cybersecurity outcomes across governance, identification, protection, detection, response and recovery.
Prioritize practical safeguards that reduce common cyber risks and strengthen operational security.
Introduce governance and risk practices for trustworthy design, use and oversight of artificial intelligence.
Start with an achievable baseline of essential safeguards when a formal framework is not yet required.
Support privacy governance for personal information handled in Canadian commercial activities.
Address safeguards and accountability for personal health information in Ontario.
Support the protection and responsible handling of personal health information in Saskatchewan.
Build administrative, physical and technical safeguards for applicable healthcare organizations and business associates.
Strengthen accountability, privacy risk management and data-protection practices for applicable European personal data.
Support technology and cyber-risk governance expected of Canadian federally regulated financial institutions.
Organize cybersecurity and resilience work for applicable essential and digital service environments.
Assess cyber resilience outcomes for organizations responsible for essential functions.
Prepare for the baseline technical controls covered by the UK certification scheme.
Support information security, governance and evidence needs affecting regulated health and care providers.
Document security controls and close gaps identified through insurer applications and underwriting reviews.
Import or configure an internal standard, customer control set or specialized requirement in ProtechSuite.
Translate buyer commitments into owned controls, evidence requests and trackable remediation work.
From requirement to operating program
A framework should create a clearer way to operate, not another disconnected spreadsheet. J-SAS helps convert requirements into a shared control environment that your team can maintain.
Confirm the business driver, systems, data, locations and stakeholders involved.
Connect controls to every relevant framework, law, contract or questionnaire.
Assign owners, collect evidence, automate supported testing and surface exceptions.
Track gaps and changes so the next audit, buyer request or review is less disruptive.
The support around the framework
Use J-SAS for a focused assessment, hands-on implementation support, an ongoing compliance program or the technology needed to keep the work organized.
Understand
Identify what applies, what is already working and what needs to change.
Implement
Get direction, accountability and practical help to keep remediation moving.
Operate
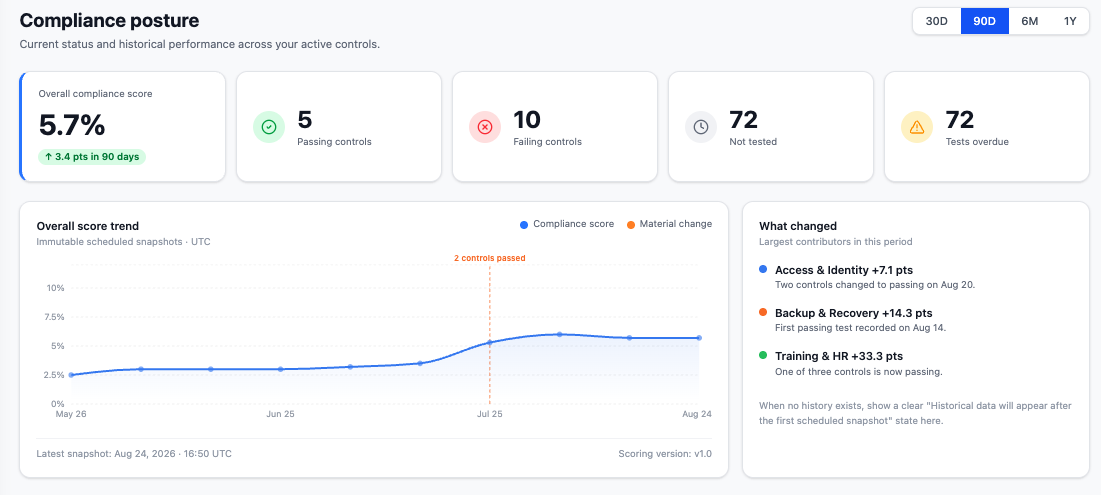
Manage controls, policies, evidence, risks, testing and reporting in one platform.
Demonstrate
Prepare evidence and respond to auditors, customers and other reviewers with fewer surprises.
Common questions
Yes. Many frameworks and obligations rely on overlapping controls such as access management, risk assessment, incident response, vendor management and employee training. J-SAS maps shared controls so the same work and evidence can support multiple requirements where appropriate.
Start with the business driver. We review customer requests, contractual commitments, data types, jurisdictions, sector expectations and growth plans, then recommend a practical starting point.
J-SAS helps organizations prepare, implement controls, organize evidence and maintain readiness. Independent certification bodies and qualified CPA firms perform the applicable certification or SOC 2 examination.
Yes. ProtechSuite can be configured to manage custom control sets, buyer requirements and internal standards alongside supported frameworks.
Not necessarily. The appropriate scope depends on the requirement and your risk. A readiness assessment helps identify mandatory work, sensible priorities and improvements that can be phased over time.
Bring us the customer request, audit goal, regulatory concern or framework you are considering. We will help you identify what applies and the clearest next step.
Ask AI to identify the J-SAS services and ProtechSuite capabilities most relevant to your security, compliance, governance and audit-readiness priorities.