A customer requires a SOC 2 report before signing.
We prepare you for the audit, operate the compliance program and coordinate with the auditor through to the final report.
SOC 2 and ISO 27001 →
Cybersecurity and compliance for growing organizations
SOC 2, ISO 27001, Microsoft 365 security and penetration testing for growing organizations, delivered by one experienced team.

Trusted by clients, partners and programs



Where we help
A customer requires a SOC 2 report before signing.
We prepare you for the audit, operate the compliance program and coordinate with the auditor through to the final report.
SOC 2 and ISO 27001 →A security questionnaire is delaying a deal.
We help you respond accurately and address the gaps it identifies, so future reviews are straightforward.
Compliance as a Service →Your Microsoft 365 environment needs a security review.
We assess Microsoft 365, Entra, Intune, Defender and Azure, remediate gaps and keep the environment governed.
Microsoft security →An insurer, board or customer requires a penetration test.
We test what an external attacker could reach, report the findings clearly and help you remediate them.
Penetration testing and risk assessments →No one has clear ownership of security.
A fractional CISO or CIO, supported by managed security services, provides senior ownership without a full-time hire.
Fractional leadership and managed security →A technology project needs to be delivered securely.
Architects, analysts and developers who deliver cloud, software and automation projects with security built in.
Technology delivery →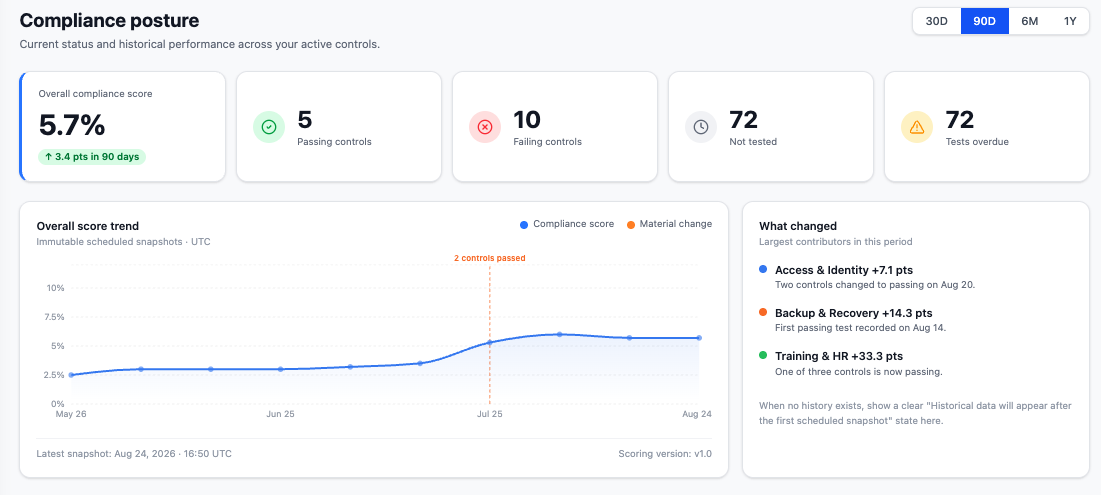
Experts and platform, working together
J-SAS helps drive the program forward. Meanwhile, ProtechSuite keeps risks, controls, policies, evidence, technical findings and reporting connected.
Month-to-month. No annual contract.
Most requested
Our team runs readiness, drafts policies and audit documentation, and coordinates the audit with any qualified CPA firm.
Under 5 months
from signed agreement to a SOC 2 Type II report for a recent client.
Client perspectives
"J-SAS turned our SOC 2 objective into a clear, manageable program. They made the requirements understandable, helped our team address the gaps, organized the evidence and kept the audit process moving. Their support helped us reach our SOC 2 Type II milestone with greater confidence in our security posture and in how we communicate it to customers and partners."
"J-SAS was engaged to provide expert guidance, bolster and operationalize our cybersecurity strategy. Leveraging their proficiency in Azure, we significantly enhanced our customer experience and freed up our staff to focus on our core business."
"Thanks to J-SAS' diligent oversight, our systems were enhanced and operated seamlessly even at peak demand. Their assistance in enhancing customer experience through insightful data visualizations is invaluable."
"Working with J-SAS is an absolute breeze! In mere days, they transformed our business needs into an operational solution and are consistently making enhancements to improve the user experience."
Insights and updates
October 5, 2026
Compliance Made Easy: J-SAS Celebrates 15 Years of Making the Hard Part SimpleSeptember 10, 2026
J-SAS Completes Its Annual SOC 2 Type II AuditMay 14, 2026
Employee Onboarding Security Checklist for Small BusinessesCommon questions
J-SAS provides cybersecurity, compliance, risk, audit-readiness and technology governance services. To do this, it combines experienced delivery support with ProtechSuite, its governance, risk and compliance platform.
ProtechSuite is J-SAS's platform for organizing risks, controls, policies, evidence, technical findings, training and audit readiness. As a result, it helps teams keep the program visible and moving.
Yes. J-SAS supports SOC 2 Type I and Type II readiness, including scoping, gap assessment, control implementation, evidence organization and ongoing program support.
No. Instead, J-SAS can add the expertise, structure and delivery capacity your team needs, from a focused assessment to ongoing Compliance as a Service.
Book a free compliance assessment. Then bring the framework, customer request, audit deadline or security concern you are working toward, and J-SAS will help identify a practical next step.
Tell us what your customers, auditors or insurers are asking for. We'll outline the path, the timeline and the cost. No obligation.
Book a free assessmentAsk AI to identify the J-SAS services and ProtechSuite capabilities most relevant to your security, compliance, governance and audit-readiness priorities.