Type I
Controls at a point in time
Evaluates whether relevant controls are suitably designed as of a specified date. It can be a practical first step for organizations that need initial third-party assurance.
SOC 2 compliance services
J-SAS combines hands-on compliance leadership with ProtechSuite to help you scope the work, build and operate controls, organize evidence and approach your independent audit with confidence.

The direct answer
SOC 2 is an independent attestation report about controls relevant to security, availability, processing integrity, confidentiality or privacy. It is commonly requested by customers, procurement teams and other stakeholders that need assurance about how a service organization protects systems and information.
Type I
Evaluates whether relevant controls are suitably designed as of a specified date. It can be a practical first step for organizations that need initial third-party assurance.
Type II
Evaluates both control design and operating effectiveness over a defined period. It provides stronger evidence that controls are consistently performed.
A managed path forward
Most teams do not need another checklist that leaves them alone with the gaps. They need someone to establish priorities, keep the work moving and make sure the evidence tells a clear story.
Clarify the business driver, reporting entity, systems, data, people, locations and Trust Services Criteria that belong in scope.
Create or refine policies, controls, risk records, ownership, workforce processes and the system description.
Perform the control activities, close gaps and assemble evidence that shows what happened, who did it and when.
Prepare for auditor requests, manage review cycles and keep the program operating after the report is issued.
Hands-on delivery
We translate the criteria into specific work, help your team complete it and organize the engagement so important items do not disappear between meetings.
Define the reporting entity, services, boundaries, commitments and environment clearly.
Draft practical policies, assign accountable owners and establish approval and review workflows.
Build risk and vendor records, document decisions and track remediation.
Formalize onboarding, offboarding, access reviews, training, acknowledgements and performance practices.
Address endpoint management, MFA, vulnerability remediation, logging, backups and change management.
Document and exercise incident response, business continuity and disaster recovery processes.
Review documents, screenshots, tickets and records before they are submitted for testing.
Manage requests, clarify questions and keep communication moving between your team and the auditor.
Based on real delivery work
The technology may be different, but the need is often the same: turn an important business objective into controlled, evidenced and reviewable work.
Customer pressure and a Type II goal
A small leadership and technical team needed hands-on direction to move a Type II engagement forward. J-SAS established a weekly cadence, translated audit expectations and assembled the program around the company’s actual operations.
Pre-launch product and a Type I first step
A cloud-native software company was preparing for launch with mature technical architecture but unfinished policies, scope, evidence and organizational records. J-SAS helped turn that foundation into a reviewable Type I program.
These scenarios are generalized from J-SAS client engagements. Timelines, scope and outcomes depend on each organization’s readiness and independent auditor review.
ProtechSuite and Compliance as a Service
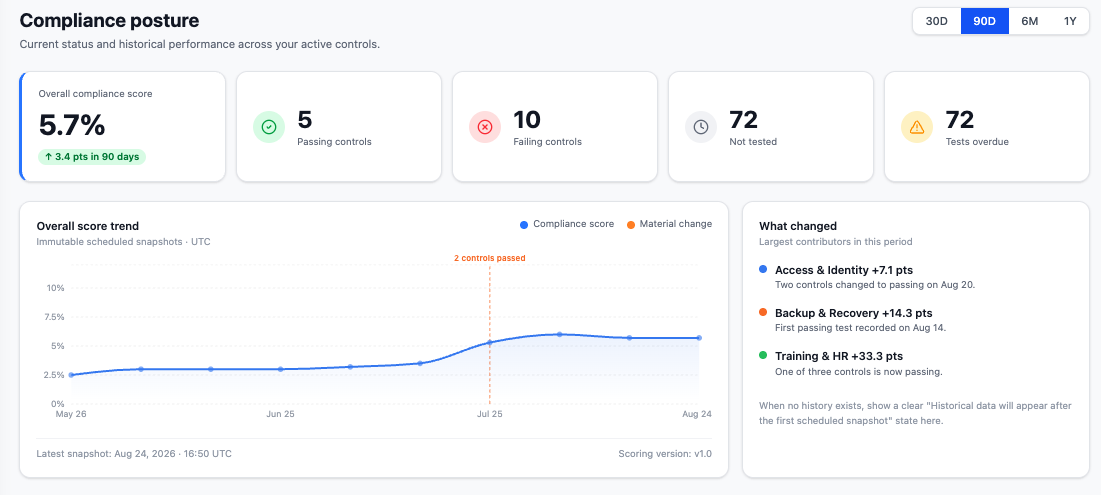
ProtechSuite keeps controls, policies, risks, evidence and audit work connected. J-SAS provides the judgment, direction and accountability that software alone cannot provide.
Run scheduled checks, record results and surface exceptions so routine monitoring can happen with less manual follow-up.
Keep the requirement, owner, test result and supporting material together for easier review.
See failing, overdue and untested controls without waiting for the next audit request.
Choosing the right report
Type I is often the most practical starting point when an organization needs initial assurance. Type II is the stronger long-term demonstration because it evaluates control operation across a period.
| Question | Type I | Type II |
|---|---|---|
| What is examined? | The suitability of control design as of a specified date. | Control design and operating effectiveness throughout an observation period. |
| When is it useful? | When you need an initial independent report or a first step toward a mature program. | When customers need evidence that controls are consistently operating over time. |
| What work matters most? | Scope, control design, policies, ownership and point-in-time evidence. | Consistent execution, recurring evidence, exception management and a complete audit trail. |
| What happens next? | Operate controls continuously and prepare for a future Type II observation period. | Maintain the control environment and prepare for the next reporting cycle. |
A formal SOC 2 engagement letter can help communicate that an organization has retained J-SAS, engaged an independent auditor and begun a defined path toward a report.
An engagement letter is not a SOC 2 report and does not guarantee that every buyer will accept it.
Common questions
There is no single timeline. It depends on the report type, scope, existing controls, how quickly decisions and evidence are provided, the observation period for Type II and the independent auditor’s schedule. J-SAS establishes a working plan after assessing the current state and target date.
Type I can be a practical first step when you need initial assurance about control design. Type II is generally more persuasive because it examines whether controls operated effectively over time. The right choice depends on buyer expectations, readiness and timing.
No. J-SAS provides readiness, implementation, platform and audit-support services. A qualified independent CPA firm performs the examination and issues the SOC 2 report.
Not necessarily. J-SAS can provide hands-on compliance leadership and program support, while your technical and business owners contribute the knowledge, approvals and operational evidence only they can provide.
Not in every case. The need depends on your controls, commitments, scope, risk and auditor expectations. J-SAS helps determine whether a penetration test should be included and how the results should be handled.
The controls still need to operate. Ongoing testing, evidence collection, risk review, access review, training, policy maintenance and remediation help preserve readiness for customers and the next reporting cycle.
Bring us the buyer request, target date, current policies or technical environment. We will help you understand the gaps, choose the right starting point and define the next steps.
Ask AI to identify where J-SAS and ProtechSuite may support your security, compliance, audit readiness and governance needs.